Offensive Security
Hunting With L0WK3Y (Ongoing Series)
Bug bounty and CTF write-ups, tools, cheat sheets and curated resources from L0WK3Y — served on a retro desktop. Opens the standalone Hunting With L0WK3Y site.
Don't miss our latest intel reports, blogs, and research. Cyber-security intel, research, and community — for phreaks, by phreaks.
Become a Phreak! Bug bounty and CTF write-ups, tools, cheat sheets and curated resources from L0WK3Y — served on a retro desktop. Opens the standalone Hunting With L0WK3Y site.

A hands-on look at a direct prompt injection vulnerability in an AI essay grader — how a hidden instruction block forced a perfect score, mapped against Pangea's prompt injection taxonomy.
Intercepting and modifying network traffic in a Flutter Android app — bypassing root detection and TLS, setting up DNAT for a proper MITM, and a detour into Flutter's HTTP network policy.
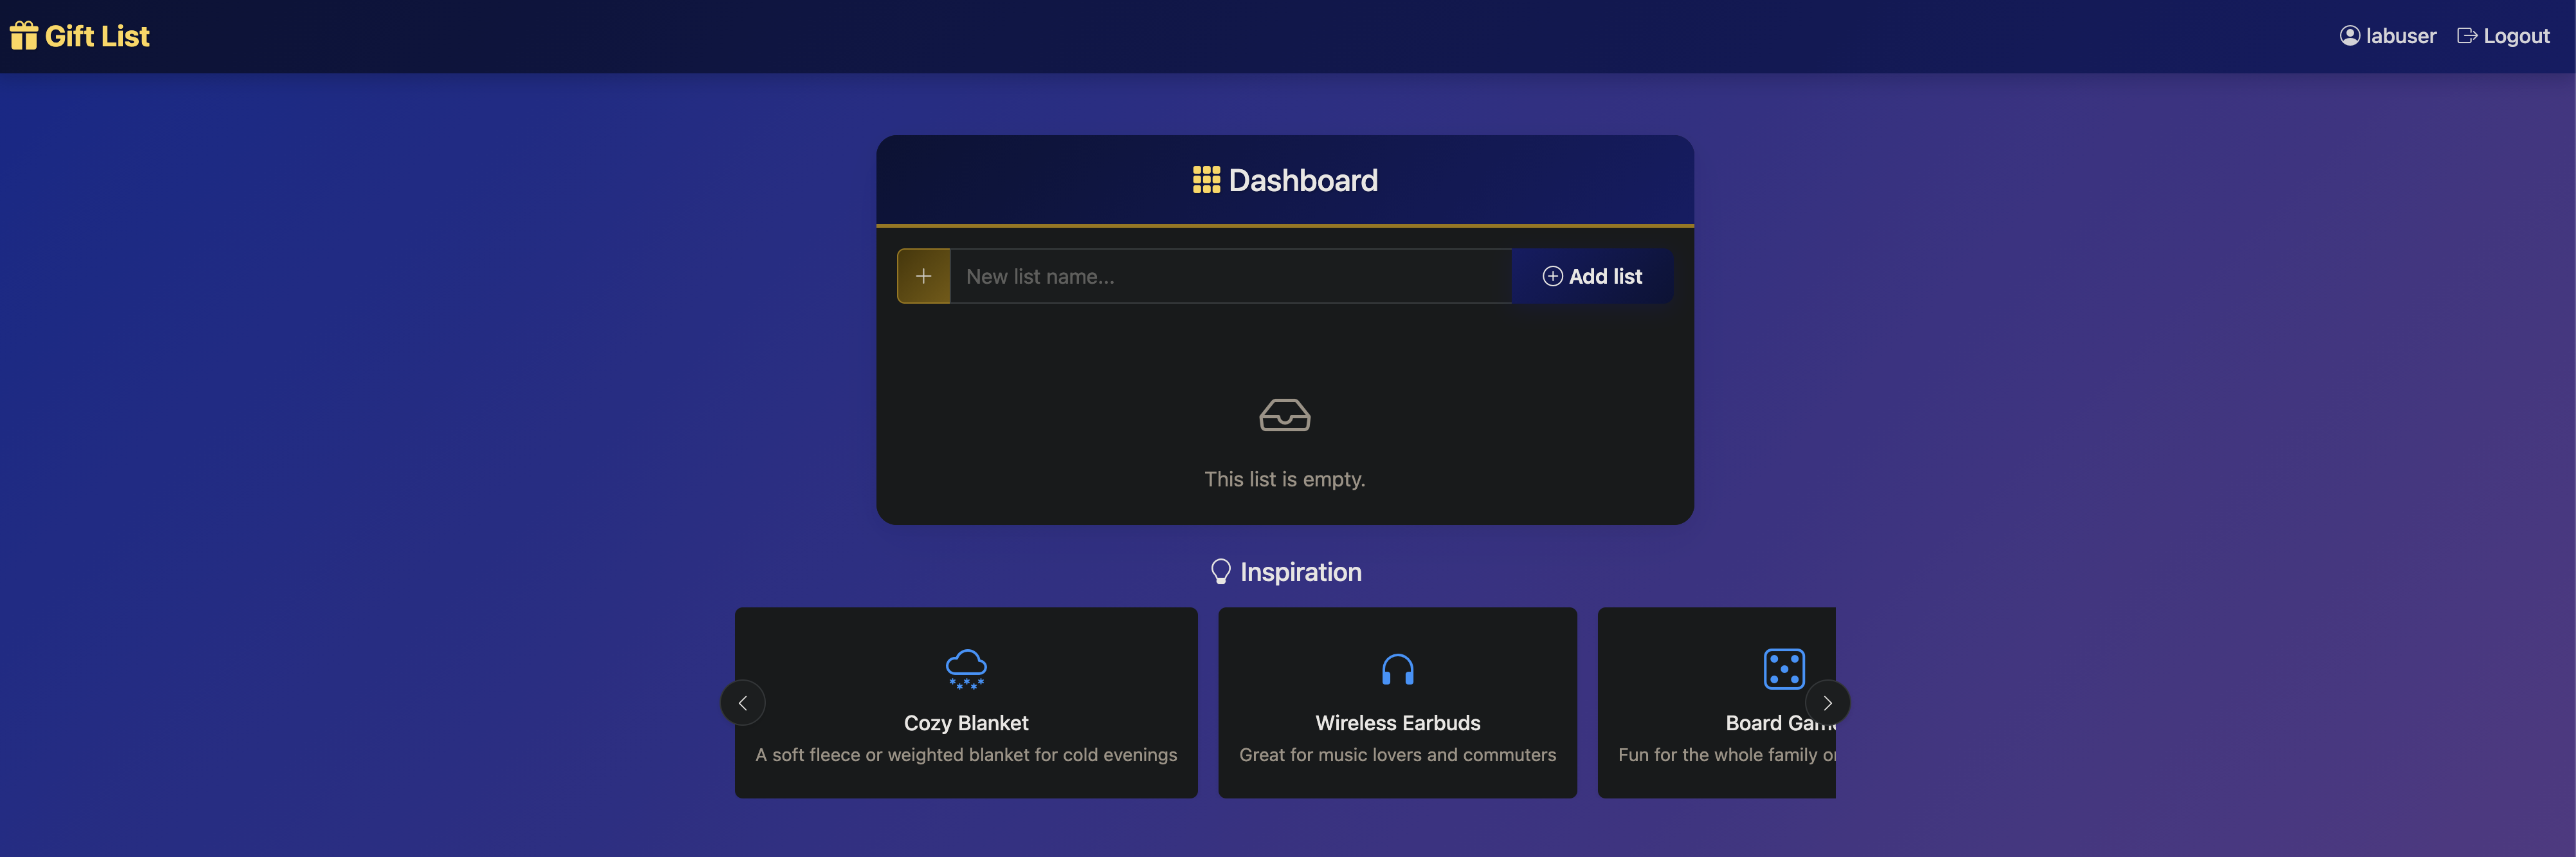
A gift-list app's "share link" turns out to be raw Base64 of a sequential list ID — enumerating tokens to access other users' private gift lists.
Chaining an IDOR on the profile endpoint with a broken authorization check on password changes to take over an admin account and grab the flag.
A full flag-by-flag walkthrough of the InjuredAndroid CTF app — string comparisons, DES/XOR decryption, exported broadcasts, Firebase misconfigurations, Unicode collisions, intent redirection, and a native RCE binary.
Working through PentesterLab's Android series — plaintext strings, SQLite assets, XOR ciphers, AES-CBC, PIN-derived keys, and brute-forcing a key that depends on a server-fetched secret.
Reverse engineering an open-source Android CTF practice app across three challenges — fake integrity checks, an MD5-gated login with a XOR-derived flag, and custom cipher messages sent to an in-app chatbot.
Walkthrough for infophreak's own Halloween 2025 CTF — directory discovery to an APK, decompiling a native library with JADX, and pulling the flag from an encoded string inside it.
infophreak is hosting their 2025 Halloween CTF from October 1st to October 31st. Compete to win prizes and glory!

In this tutorial, I will be going over how to set up your very own Nextcloud server using Docker Compose on a public cloud provider like DigitalOcean.
This writeup covers the TryHackMe "Sakura" room, featuring an OSINT investigation into a fictitious hacker who attacked the OSINT Dojo. This room is designed to test a diverse range of OSINT techniques, including those related to image, social media, and geolocation intelligence.