Offensive Security
Hunting With L0WK3Y (Ongoing Series)
Bug bounty and CTF write-ups, tools, cheat sheets and curated resources from L0WK3Y — served on a retro desktop. Opens the standalone Hunting With L0WK3Y site.
Explore the latest tools, techniques, and strategies used by ethical hackers to fortify defenses by thinking like an attacker. From pen-testing methodologies to exploit development and vulnerability analysis, we cover crucial topics to arm you with the knowledge needed to protect your systems. Our insights and practical guides aim to educate and inspire both beginners and seasoned professionals in the ever-evolving battle against cyber threats.
Bug bounty and CTF write-ups, tools, cheat sheets and curated resources from L0WK3Y — served on a retro desktop. Opens the standalone Hunting With L0WK3Y site.

A hands-on look at a direct prompt injection vulnerability in an AI essay grader — how a hidden instruction block forced a perfect score, mapped against Pangea's prompt injection taxonomy.
Intercepting and modifying network traffic in a Flutter Android app — bypassing root detection and TLS, setting up DNAT for a proper MITM, and a detour into Flutter's HTTP network policy.
A gift-list app's "share link" turns out to be raw Base64 of a sequential list ID — enumerating tokens to access other users' private gift lists.
Chaining an IDOR on the profile endpoint with a broken authorization check on password changes to take over an admin account and grab the flag.
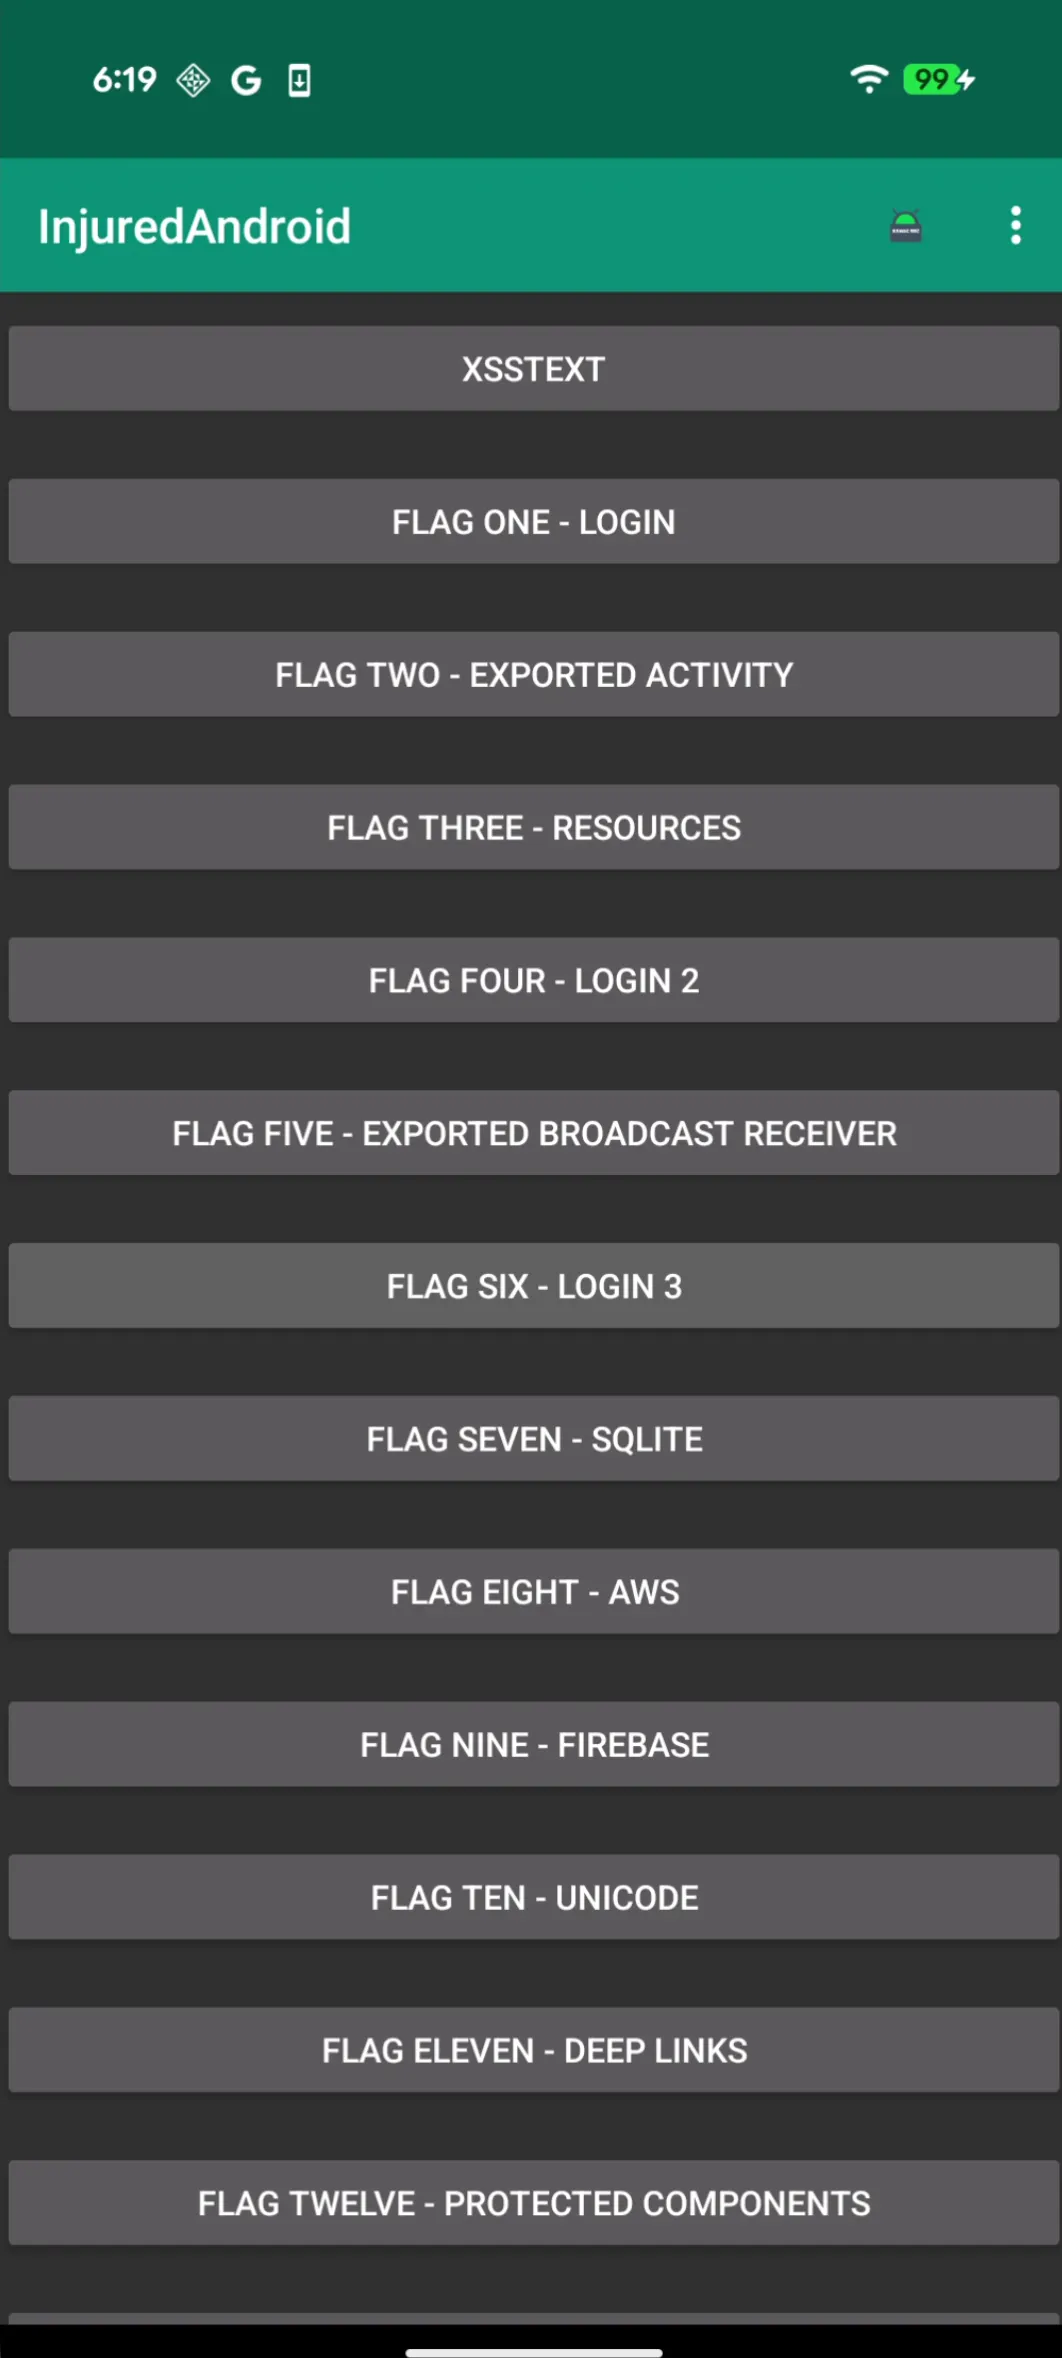
A full flag-by-flag walkthrough of the InjuredAndroid CTF app — string comparisons, DES/XOR decryption, exported broadcasts, Firebase misconfigurations, Unicode collisions, intent redirection, and a native RCE binary.
Working through PentesterLab's Android series — plaintext strings, SQLite assets, XOR ciphers, AES-CBC, PIN-derived keys, and brute-forcing a key that depends on a server-fetched secret.
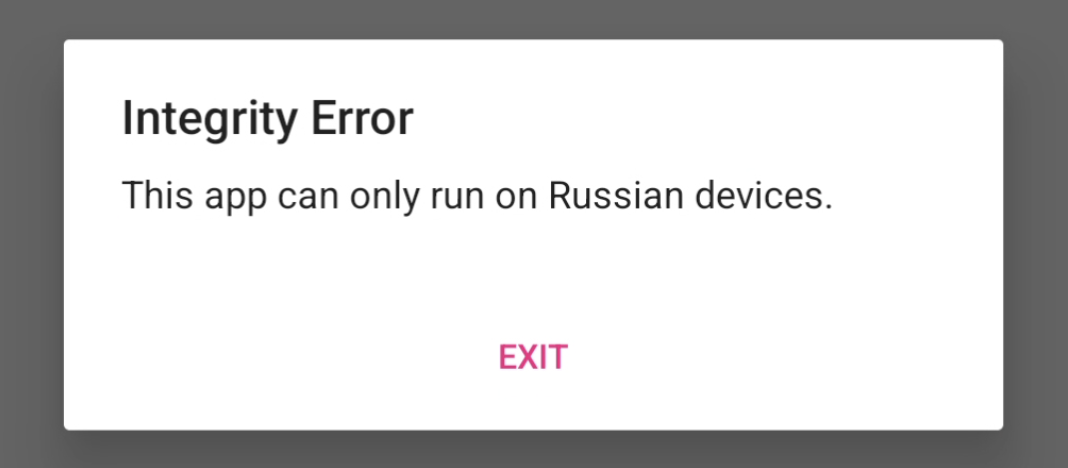
Reverse engineering an open-source Android CTF practice app across three challenges — fake integrity checks, an MD5-gated login with a XOR-derived flag, and custom cipher messages sent to an in-app chatbot.
Walkthrough for infophreak's own Halloween 2025 CTF — directory discovery to an APK, decompiling a native library with JADX, and pulling the flag from an encoded string inside it.

This article covers a post-incident OSINT investigation that linked a recent business email compromise back to an Australian carpet company, due to a DNS registration mishap by the attacker. Persistence and pivoting are key for investigators!

A bird's eye view of the Dark Web focused on the essentials. If the inner workings of the Dark Web remain a mystery to you, this post was made to change that.

This article demonstrates how an Azure VM can be configured as a Netcat reverse shell listener, detailing setup steps (opening ports, running nc), potential security risks, and mitigation strategies. It highlights detection methods via Azure logging and best practices to prevent misuse.

This lab's administration interface has an authentication bypass vulnerability, but it is impractical to exploit without knowledge of a custom HTTP header used by the front-end.

This lab leaks its source code via backup files in a hidden directory. To solve the lab, identify and submit the database password, which is hard-coded in the leaked source code.

This lab contains a debug page that discloses sensitive information about the application. To solve the lab, obtain and submit the SECRET_KEY environment variable.

This lab discloses sensitive information via its version control history. To solve the lab, obtain the password for the administrator user then log in and delete the user carlos.

This article details the findings of two studies that highlight how security vulnerabilities in publicly-accessible LLMs can present a threat to public security through the proliferation of malicious knowledge, guidance in committing illegal activities, and generation of malicious content.

This lab's verbose error messages reveal that it is using a vulnerable version of a third-party framework. To solve the lab, obtain and submit the version number of this framework.